Quiz Entry - updated: 2026.10.26
How do the OSI model, ISO 27001, the ISMS, OWASP and CSA each act on the security of a cyber system?
CSA defines construction requirements, the ISMS defines management requirements, ISO 27001 defines the requirements for the ISMS, the OSI model describes the network, and the OWASP Top 10 points out weaknesses (web only).
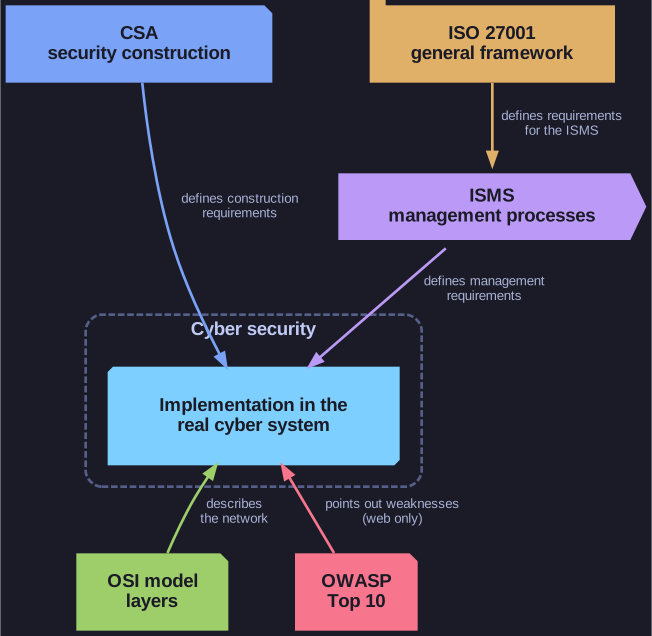
* Five sources, one target. Only CSA and the ISMS set requirements on the system directly; ISO 27001 acts through the ISMS. *
All of them converge on the cyber security implementation of a real system:
| Source | Relationship to the system |
|---|---|
| CSA (cyber security construction) | Defines construction requirements |
| ISMS (information security management, its processes) | Defines management requirements |
| ISO 27001 (general framework) | Defines the requirements for the ISMS, so it acts on the system only indirectly |
| OSI model (layers) | Describes the network |
| OWASP Top 10 | Points out weaknesses, for web applications only |
The picture shows why CSA cannot work alone: construction and management come from different sources, and a good architecture has to satisfy both.
Go deeper:
 BSI — IT-Grundschutz — the German federal method that joins an ISMS with concrete technical and organisational measures, and leads to an ISO 27001 certificate.
- SABSA — Wikipedia — a security architecture method that carries business requirements down through design layers to operations.