What happens if you reuse a One-Time Pad key for two different messages?
Reusing a OTP key completely destroys its security — an attacker can XOR the two ciphertexts together to eliminate the key and obtain the XOR of the two plaintexts.
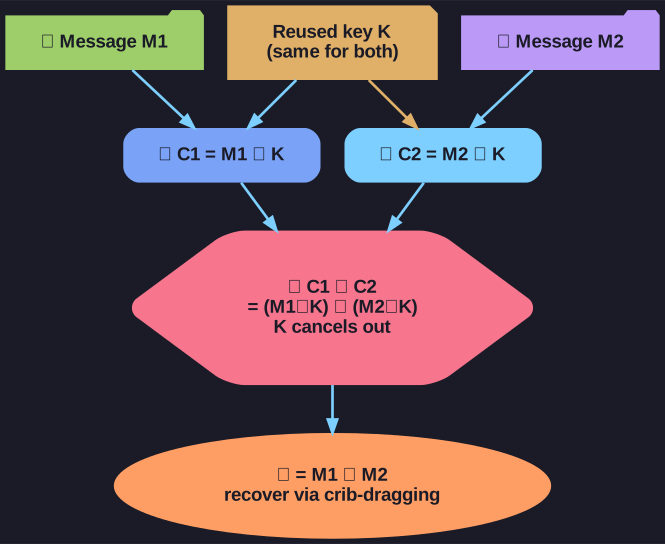
* Reuse the pad and the key cancels: $C_1 \oplus C_2 = M_1 \oplus M_2$, recoverable by crib-dragging. *
The attack:
$$\begin{aligned} C_1 &= M_1 \oplus K \\ C_2 &= M_2 \oplus K \\ C_1 \oplus C_2 &= (M_1 \oplus K) \oplus (M_2 \oplus K) = M_1 \oplus M_2 \end{aligned}$$
The key $K$ cancels out! Now the attacker has $M_1 \oplus M_2$, and using frequency analysis and known-plaintext techniques (known as "crib dragging"), they can often recover both messages.
Real-world failure: The VENONA project — the NSA broke Soviet spy communications because some OTP key pages were reused. This shows that even the theoretically perfect cipher fails catastrophically with key reuse.
Tip: This same principle applies to all stream ciphers — never reuse a keystream, whether it's from an OTP or a PRNG-based stream cipher.
Go deeper:
 VENONA project (Wikipedia) — how reused Soviet one-time-pad pages were broken.