Quiz Entry - updated: 2026.10.26
What makes up the "toolbox" of security-by-obscurity?
Naivety, ignorance and a lack of imagination: believing a system is safe because it is old, rare or exotic; not knowing about hidden admin interfaces, debug APIs or open ports; and not being able to imagine what could go wrong, often combined with overestimating one's own abilities.
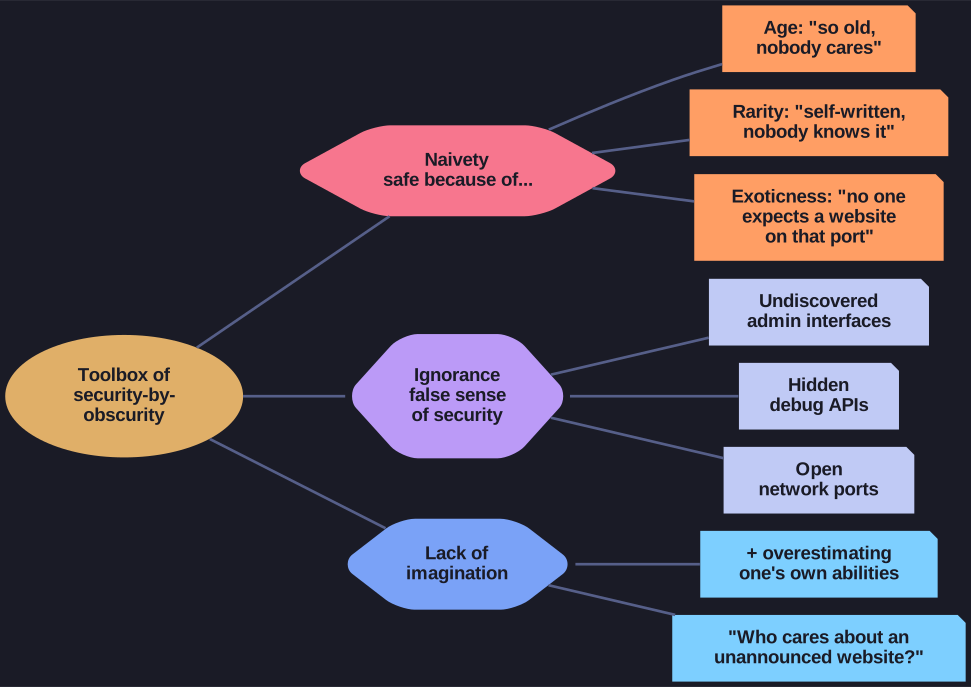
* Naivety, ignorance and a lack of imagination each give a false sense of security. *
- Naivety: the system is considered safe because of its
- age: "My system is so old, nobody is interested in it", "there are no exploits for it",
- low distribution: "The system is largely unknown", "I wrote it myself, nobody can know it",
- perceived exoticness: "Nobody expects a website on that port."
- Ignorance also gives a false sense of security: undiscovered admin interfaces, hidden debug APIs, open network ports.
- Lack of imagination, often with overestimation of one's own abilities: a developer who cannot imagine what an open debug API known only to them could lead to sees no reason to protect it. The business has its equivalent: "Who would care about an unimportant website whose existence we never announced?"
Go deeper:
 CWE-489 — Active Debug Code — the forgotten debug interface as a catalogued weakness.
- Shodan (website) — Wikipedia — a search engine that indexes exposed devices and services, however obscure.