Quiz Entry - updated: 2026.10.26
Which three general models and standards matter for applied cyber security architecture, and how do they differ in status?
The ISO/OSI reference model (a model that became a norm, 1983), ISO 27001 (a norm from the ISO 27000 family, 2005, revised 2013 and 2022) and the OWASP Top 10 (a quasi-standard, updated irregularly).
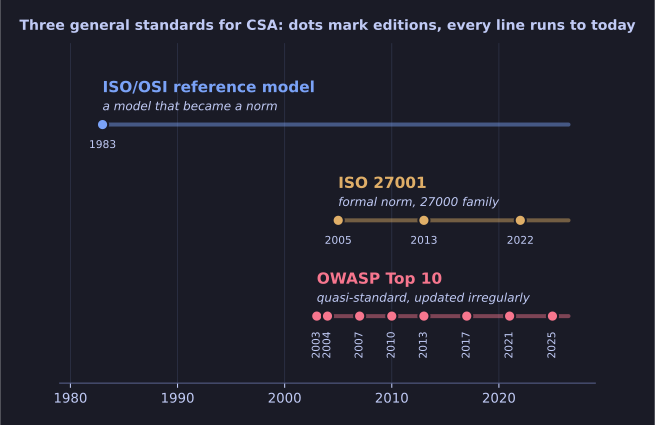
* Three standards, three kinds of status. The dots are editions, and all three are still in use today. *
| Status | Since | Covers | |
|---|---|---|---|
| ISO/OSI reference model | Model as a norm (ISO standard) | 1983 | Network communication in layers |
| ISO 27001 | Formal norm from the 27000 family | 2005, revised 2013, 2022 | Requirements for an information security management system (ISMS) |
| OWASP Top 10 | Quasi-standard (de facto, from a non-profit) | Updated irregularly | The most common security risks in web development |
The difference in status matters in practice: an ISO norm can be audited and certified against; the OWASP Top 10 is a widely accepted reference, not a formal norm. Its editions came at irregular intervals, from the first list in 2003 to the 2025 edition.
Go deeper:
 ISO/IEC 27001 — Wikipedia — the three editions and how certification audits by independent bodies work.
- OWASP — Wikipedia — the non-profit behind the Top 10, and why regulators and PCI DSS cite a list that is not a formal norm.