Question
What is Shamir Secret Sharing, and how does it relate to Multi-Party Computation?
Answer
Shamir Secret Sharing (1979) splits a secret s into n shares such that any k shares can reconstruct s, but fewer than k shares reveal nothing. It's the foundational primitive that many MPC protocols use to distribute computation safely.
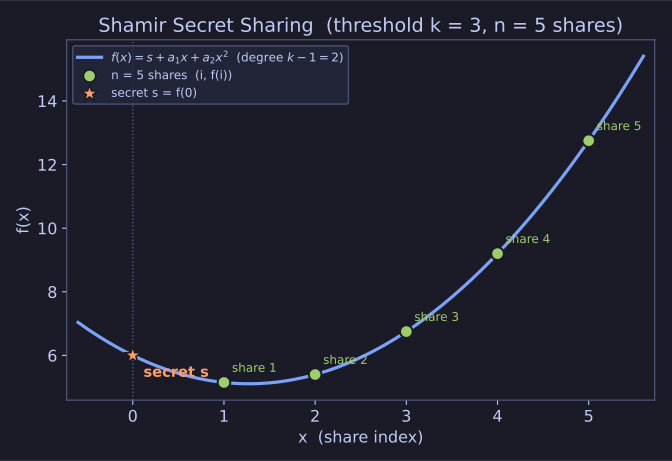
* The secret is the curve at x=0; any k=3 of n=5 shares reconstruct it, fewer reveal nothing. *
How it works (informally):
- To share a secret
swith thresholdk, pick a random polynomial of degreek−1whose constant term iss:f(x) = s + a₁·x + a₂·x² + … + a_{k-1}·x^{k-1}(all arithmetic mod a large prime) - Each shareholder
ireceives the share(i, f(i)). - To recover
s, anykshareholders interpolate the polynomial atx=0(Lagrange interpolation) and read off the constant term.
Properties:
- Information-theoretically secure: with
k−1shares, the secret is literally uniformly distributed — no computational assumption. - Linear: adding two shared secrets, or multiplying by a constant, can be done locally on each share. Multiplying two shared secrets requires more work — and that's where MPC protocols start to get clever.
Where it shows up:
- HashiCorp Vault, AWS KMS, Google Cloud HSM: master keys are stored as Shamir shares across hardware modules and operators.
- MPC wallets (Fireblocks, ZenGo): the private key never exists in one place — it's permanently held as shares.
- The Zettelchen-voting protocol (paper-slip MPC voting) is essentially Shamir-style additive secret sharing with threshold = all participants.
Tip: Shamir's "any k-of-n" property is the most-cited use of polynomial interpolation in cryptography. The same math underlies Reed-Solomon error correction (every CD and QR code uses it).
Go deeper:
 Shamir's secret sharing (Wikipedia) — the polynomial/Lagrange k-of-n construction.
- Secure multi-party computation (Wikipedia) — how secret sharing underpins MPC.

Note saved — thanks!
Question
What are the BSI-Standards and the IT-Grundschutz-Kompendium, and how do they fit together?
Answer
The BSI-Standards (200-1 / 200-2 / 200-3 / 100-4) describe the methodology of an ISMS and IT-Grundschutz. The Kompendium is the content library: 80+ Bausteine (building blocks), each with threats and concrete safeguards.
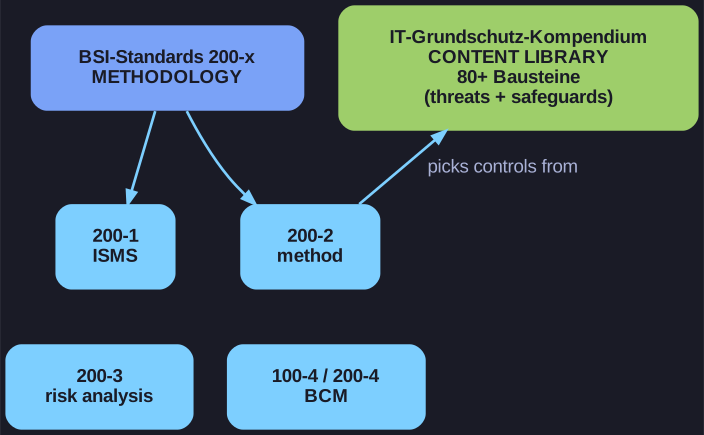
* Split of labour: the 200-x standards give the method; the Kompendium supplies the actual controls (Bausteine). *
| BSI-Standard | Topic |
|---|---|
| 200-1 | Management systems for information security (ISMS) |
| 200-2 | IT-Grundschutz methodology |
| 200-3 | Risk analysis based on IT-Grundschutz |
| 100-4 | Notfallmanagement (emergency / business continuity) |
The IT-Grundschutz-Kompendium structure:
| Kapitel | Content |
|---|---|
| Kapitel 1 | Vorspann (intro) |
| Kapitel 2 | Schichtenmodell und Modellierung |
| Elementare Gefährdungen (47 generic threats) | |
| Process-Bausteine: ISMS, ORP, CON, OPS, DER | |
| System-Bausteine: IND, APP, SYS, NET, INF |
The Kompendium shrank from 4000+ pages to 816 pages by consolidating implementation guidance into Bausteine.
Tip: Don't read the Kompendium cover-to-cover. The right way is: pick the Bausteine that match your environment (e.g., NET.1.1 Netzarchitektur, APP.5.3 E-Mail-Server), and use those as your control roadmap.
Go deeper:
- BSI-Standards 200-1/200-2/200-3/200-4 (official, DE) — the methodology standards, each summarised on the source page.
- IT-Grundschutz-Kompendium (official, DE) — the content library of 80+ Bausteine (building blocks) and its ten layers.
Note saved — thanks!