Question
What distinguishes Waterfall from Agile approaches in handling changing requirements?
Answer
Waterfall locks requirements in up front and resists change; Agile gathers them iteratively and welcomes change every sprint.
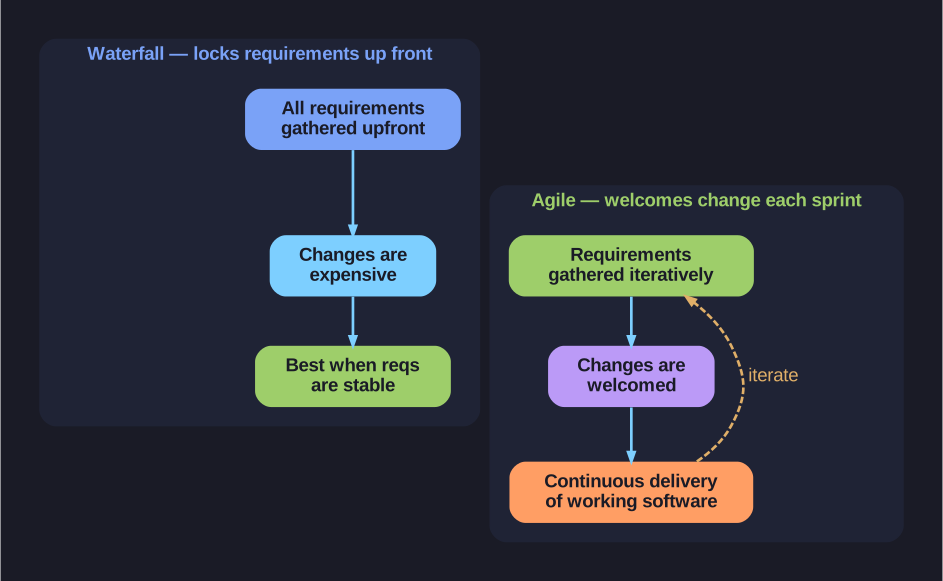
* Waterfall locks requirements up front; Agile loops each iteration and welcomes change. *
Waterfall:
- All requirements gathered upfront
- Changes are expensive and difficult
- Works when requirements are stable and well-understood
- Sequential phases with clear milestones
Agile:
- Requirements gathered iteratively
- Changes are welcomed and expected
- Works when requirements are evolving or uncertain
- Continuous delivery of working software
Security implication:
- Waterfall: Security requirements defined early, less flexibility
- Agile: Security must be integrated into each sprint, continuous security testing
Note saved — thanks!
Question
What was the Morris Worm and what did it demonstrate about buffer overflows?
Answer
The 1988 Morris Worm was the first major internet worm; by exploiting buffer overflows in Unix services it proved such bugs could give remote code execution and take down machines network-wide.
The Morris Worm (1988) was the first major internet worm, written by Robert Morris as an experiment to estimate internet size. It spread using:
- Dictionary attacks on weak passwords
- Buffer overflow exploits in Unix services (fingerd, sendmail)
What went wrong: A bug caused it to reinfect machines repeatedly, consuming all resources and crashing ~6,000 computers (~10% of the internet at the time).
Security significance:
- Demonstrated that buffer overflows could achieve remote code execution
- Showed that a single vulnerability could have cascading network-wide effects
- Led to creation of CERT (Computer Emergency Response Team)
- First prosecution under Computer Fraud and Abuse Act
The Morris Worm proved that theoretical vulnerabilities could cause real-world catastrophic damage.
Go deeper:
 Morris worm (Wikipedia) — corroborates fingerd/sendmail exploits, ~6,000 machines, CERT, first CFAA conviction.
Note saved — thanks!